Govern Every AI System Running In Your Company
Tahara AI discovers every AI system in your environment, checks it against the frameworks that actually apply, and produces the evidence to prove it, continuously rather than once a year.
Outcomes You Can Measure, Not Just Promises You're Told
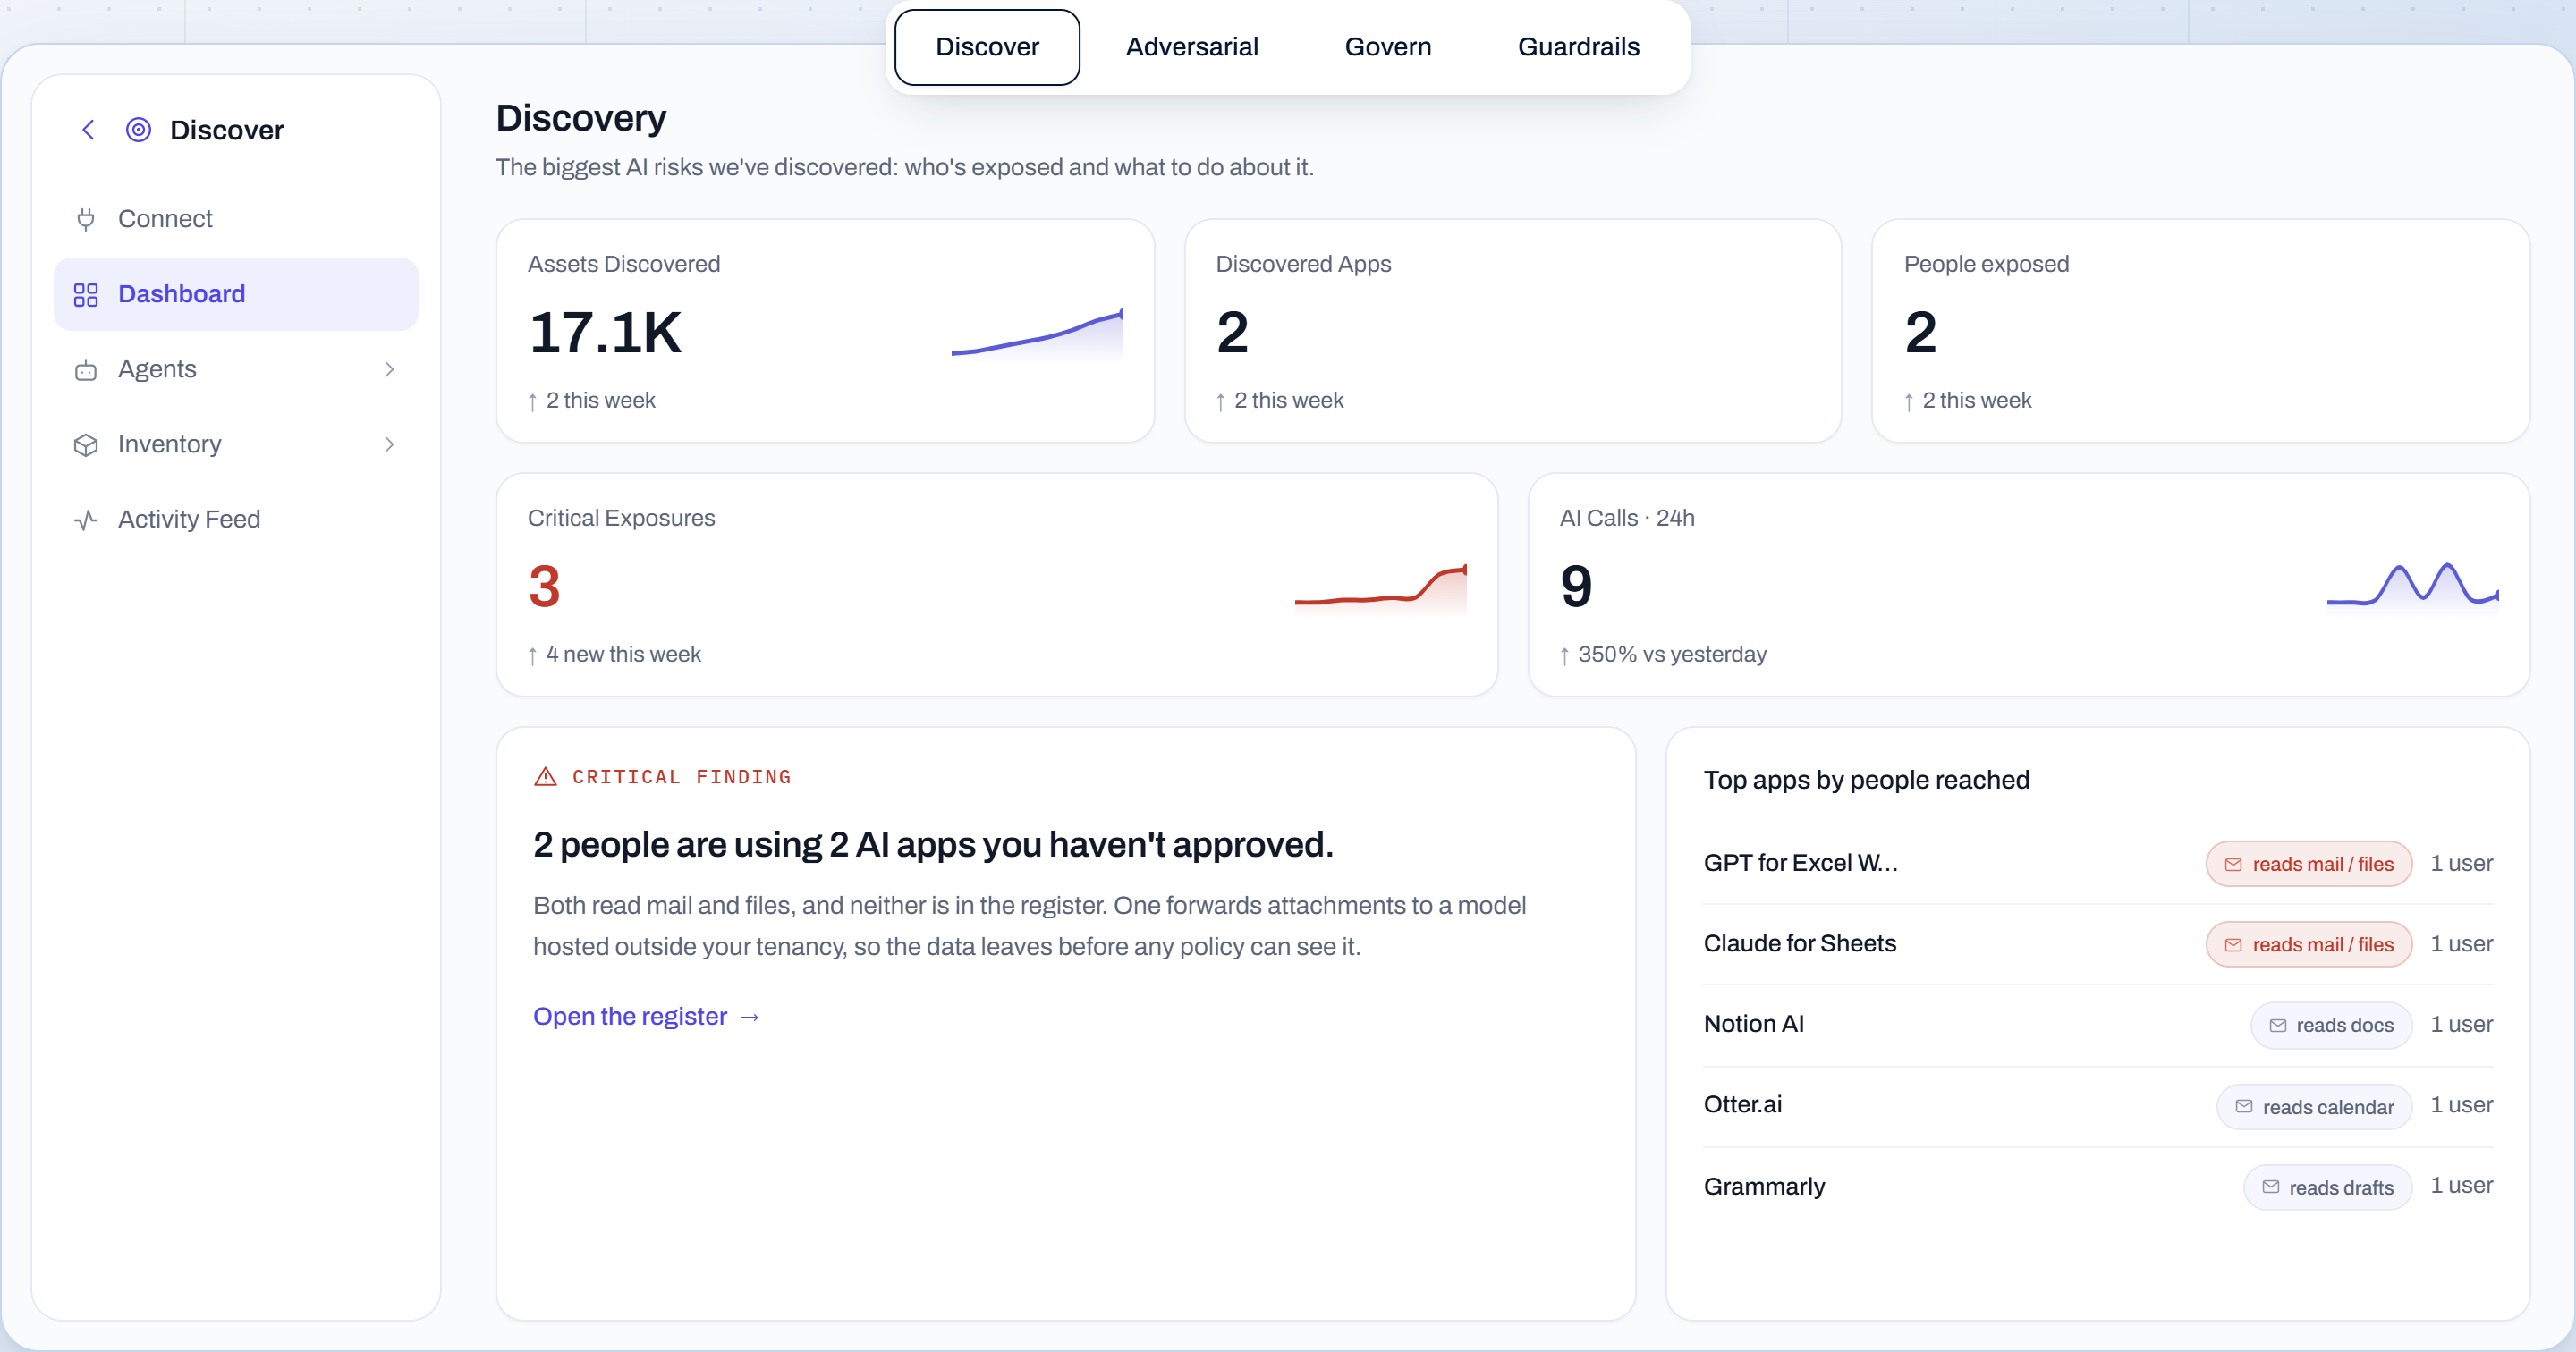
Find Every AI System, Not Just the Ones You Approved
AI systems get built in-house, bundled into tools you already pay for, or shipped before anyone signed off. A read-only collector runs inside your own boundary, under your own credentials, and finds every one within a day.
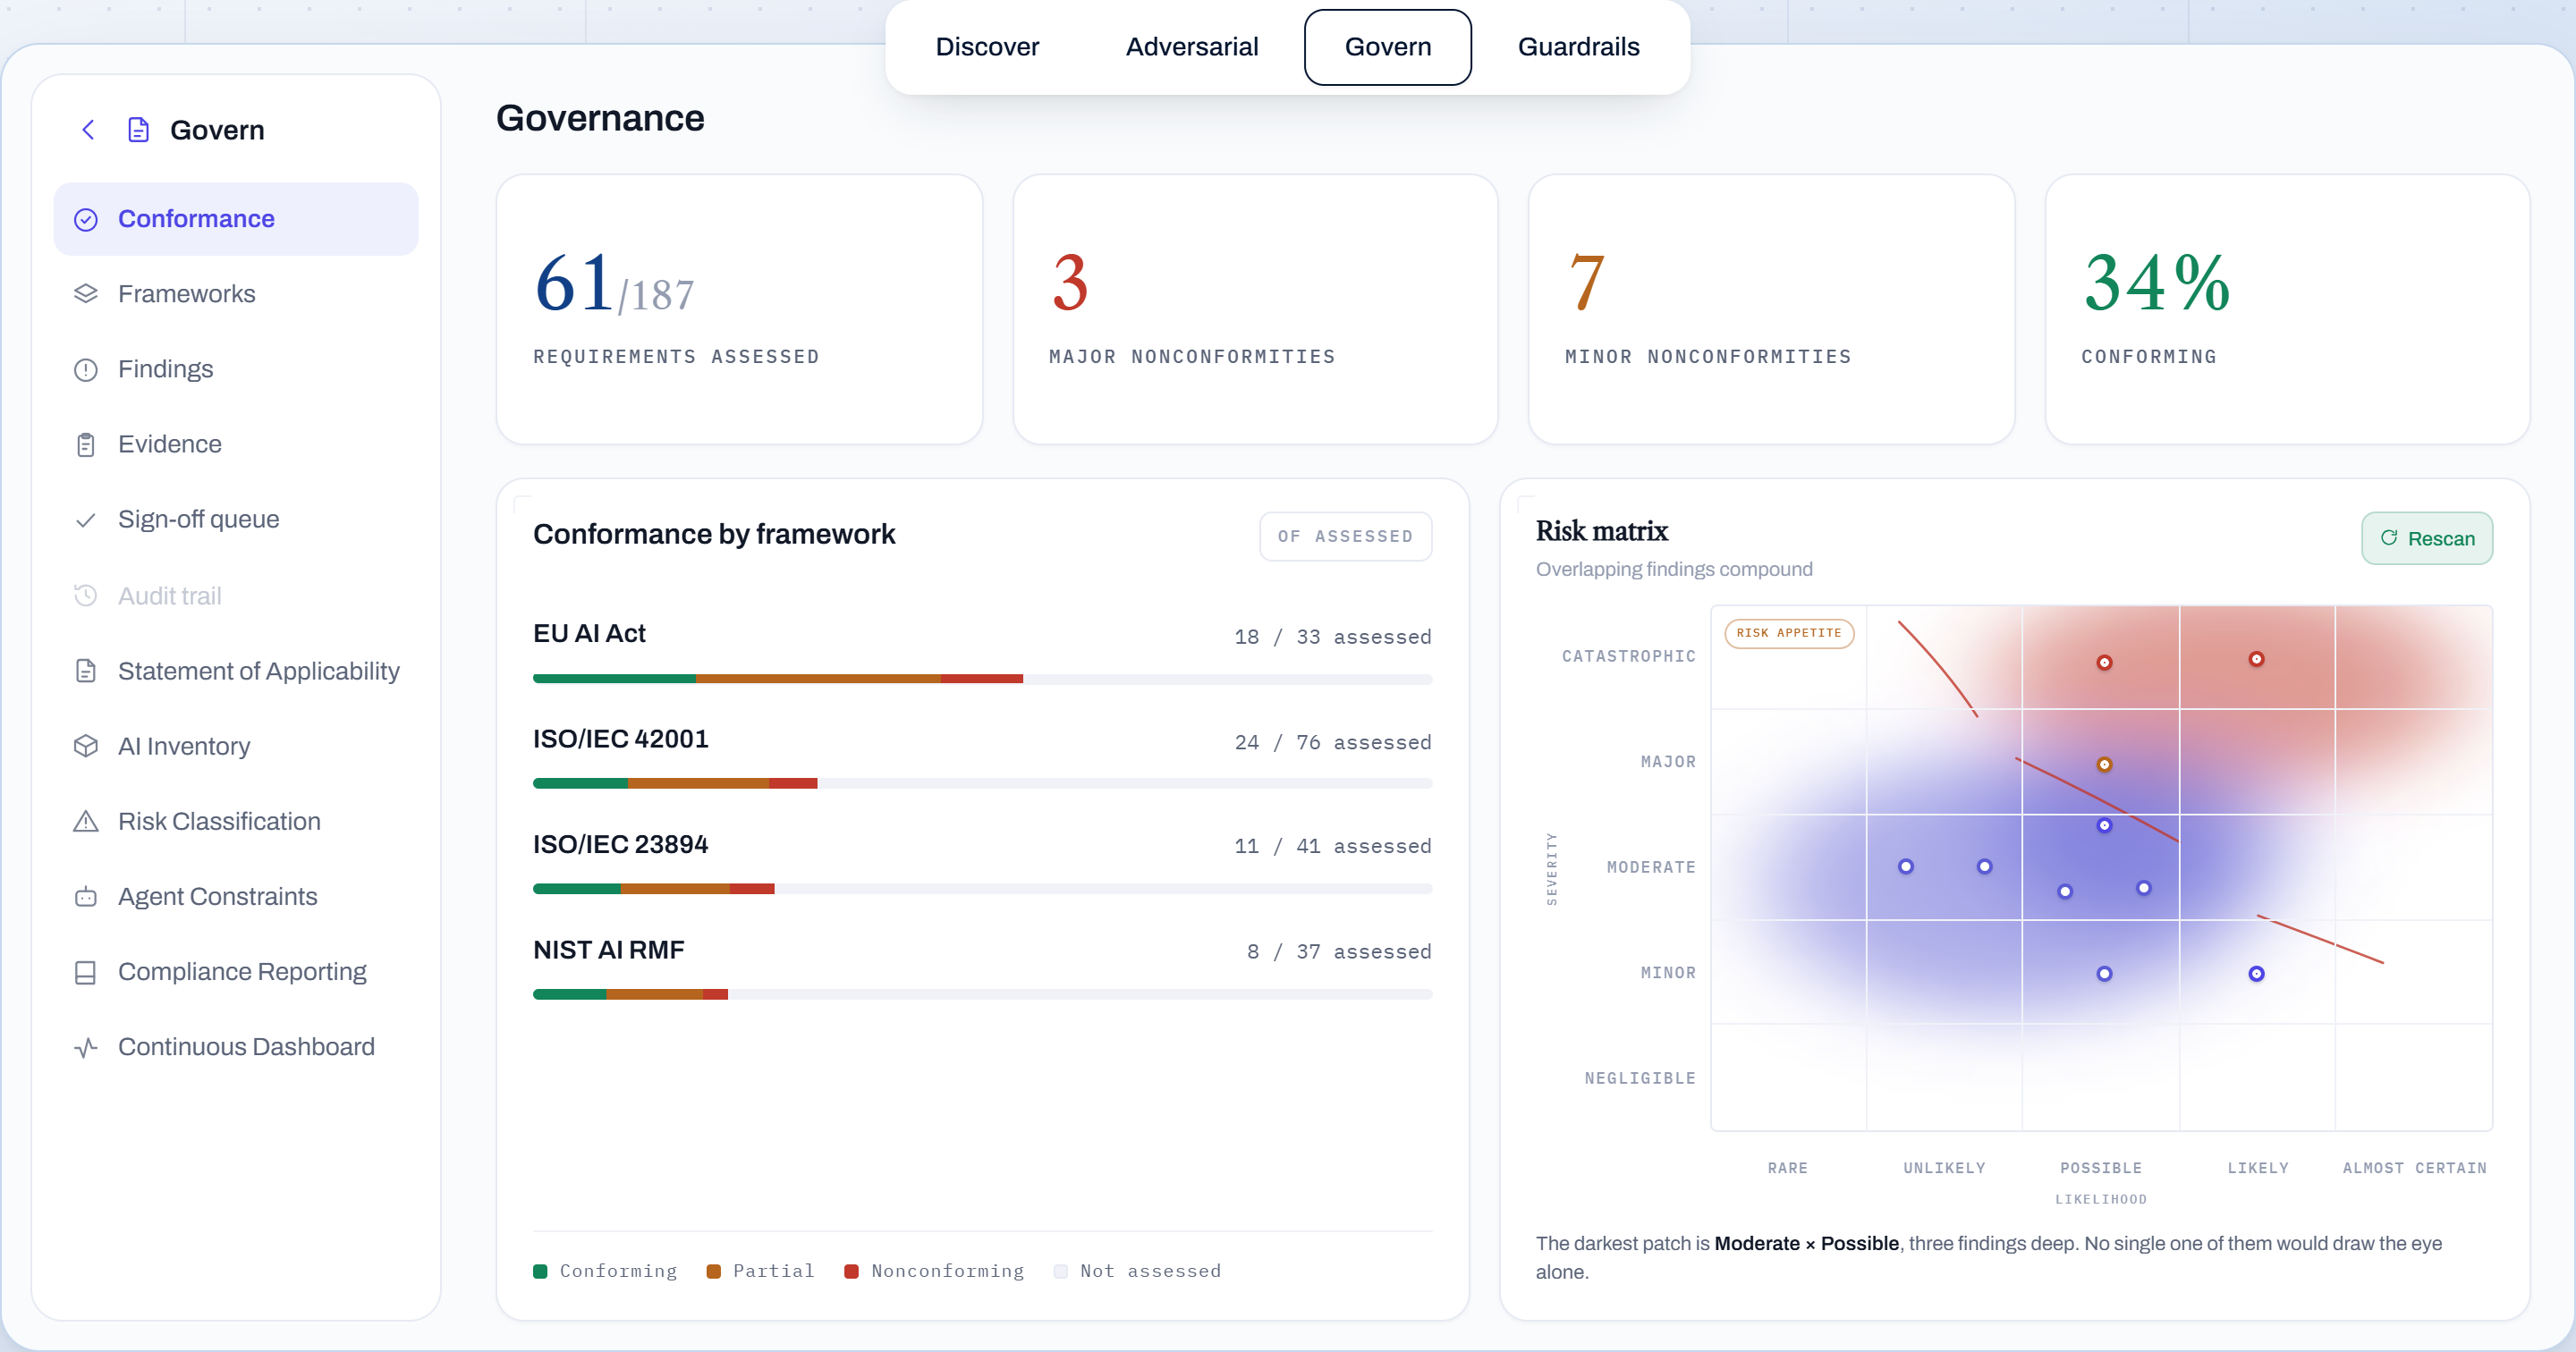
Map Every System to the Law That Actually Applies
A policy that says the right thing isn’t a system that does it. Every requirement is checked against your live system, and only marked "Conforming" once a named person confirms it on the record. A machine’s observation can raise a finding, never close one.
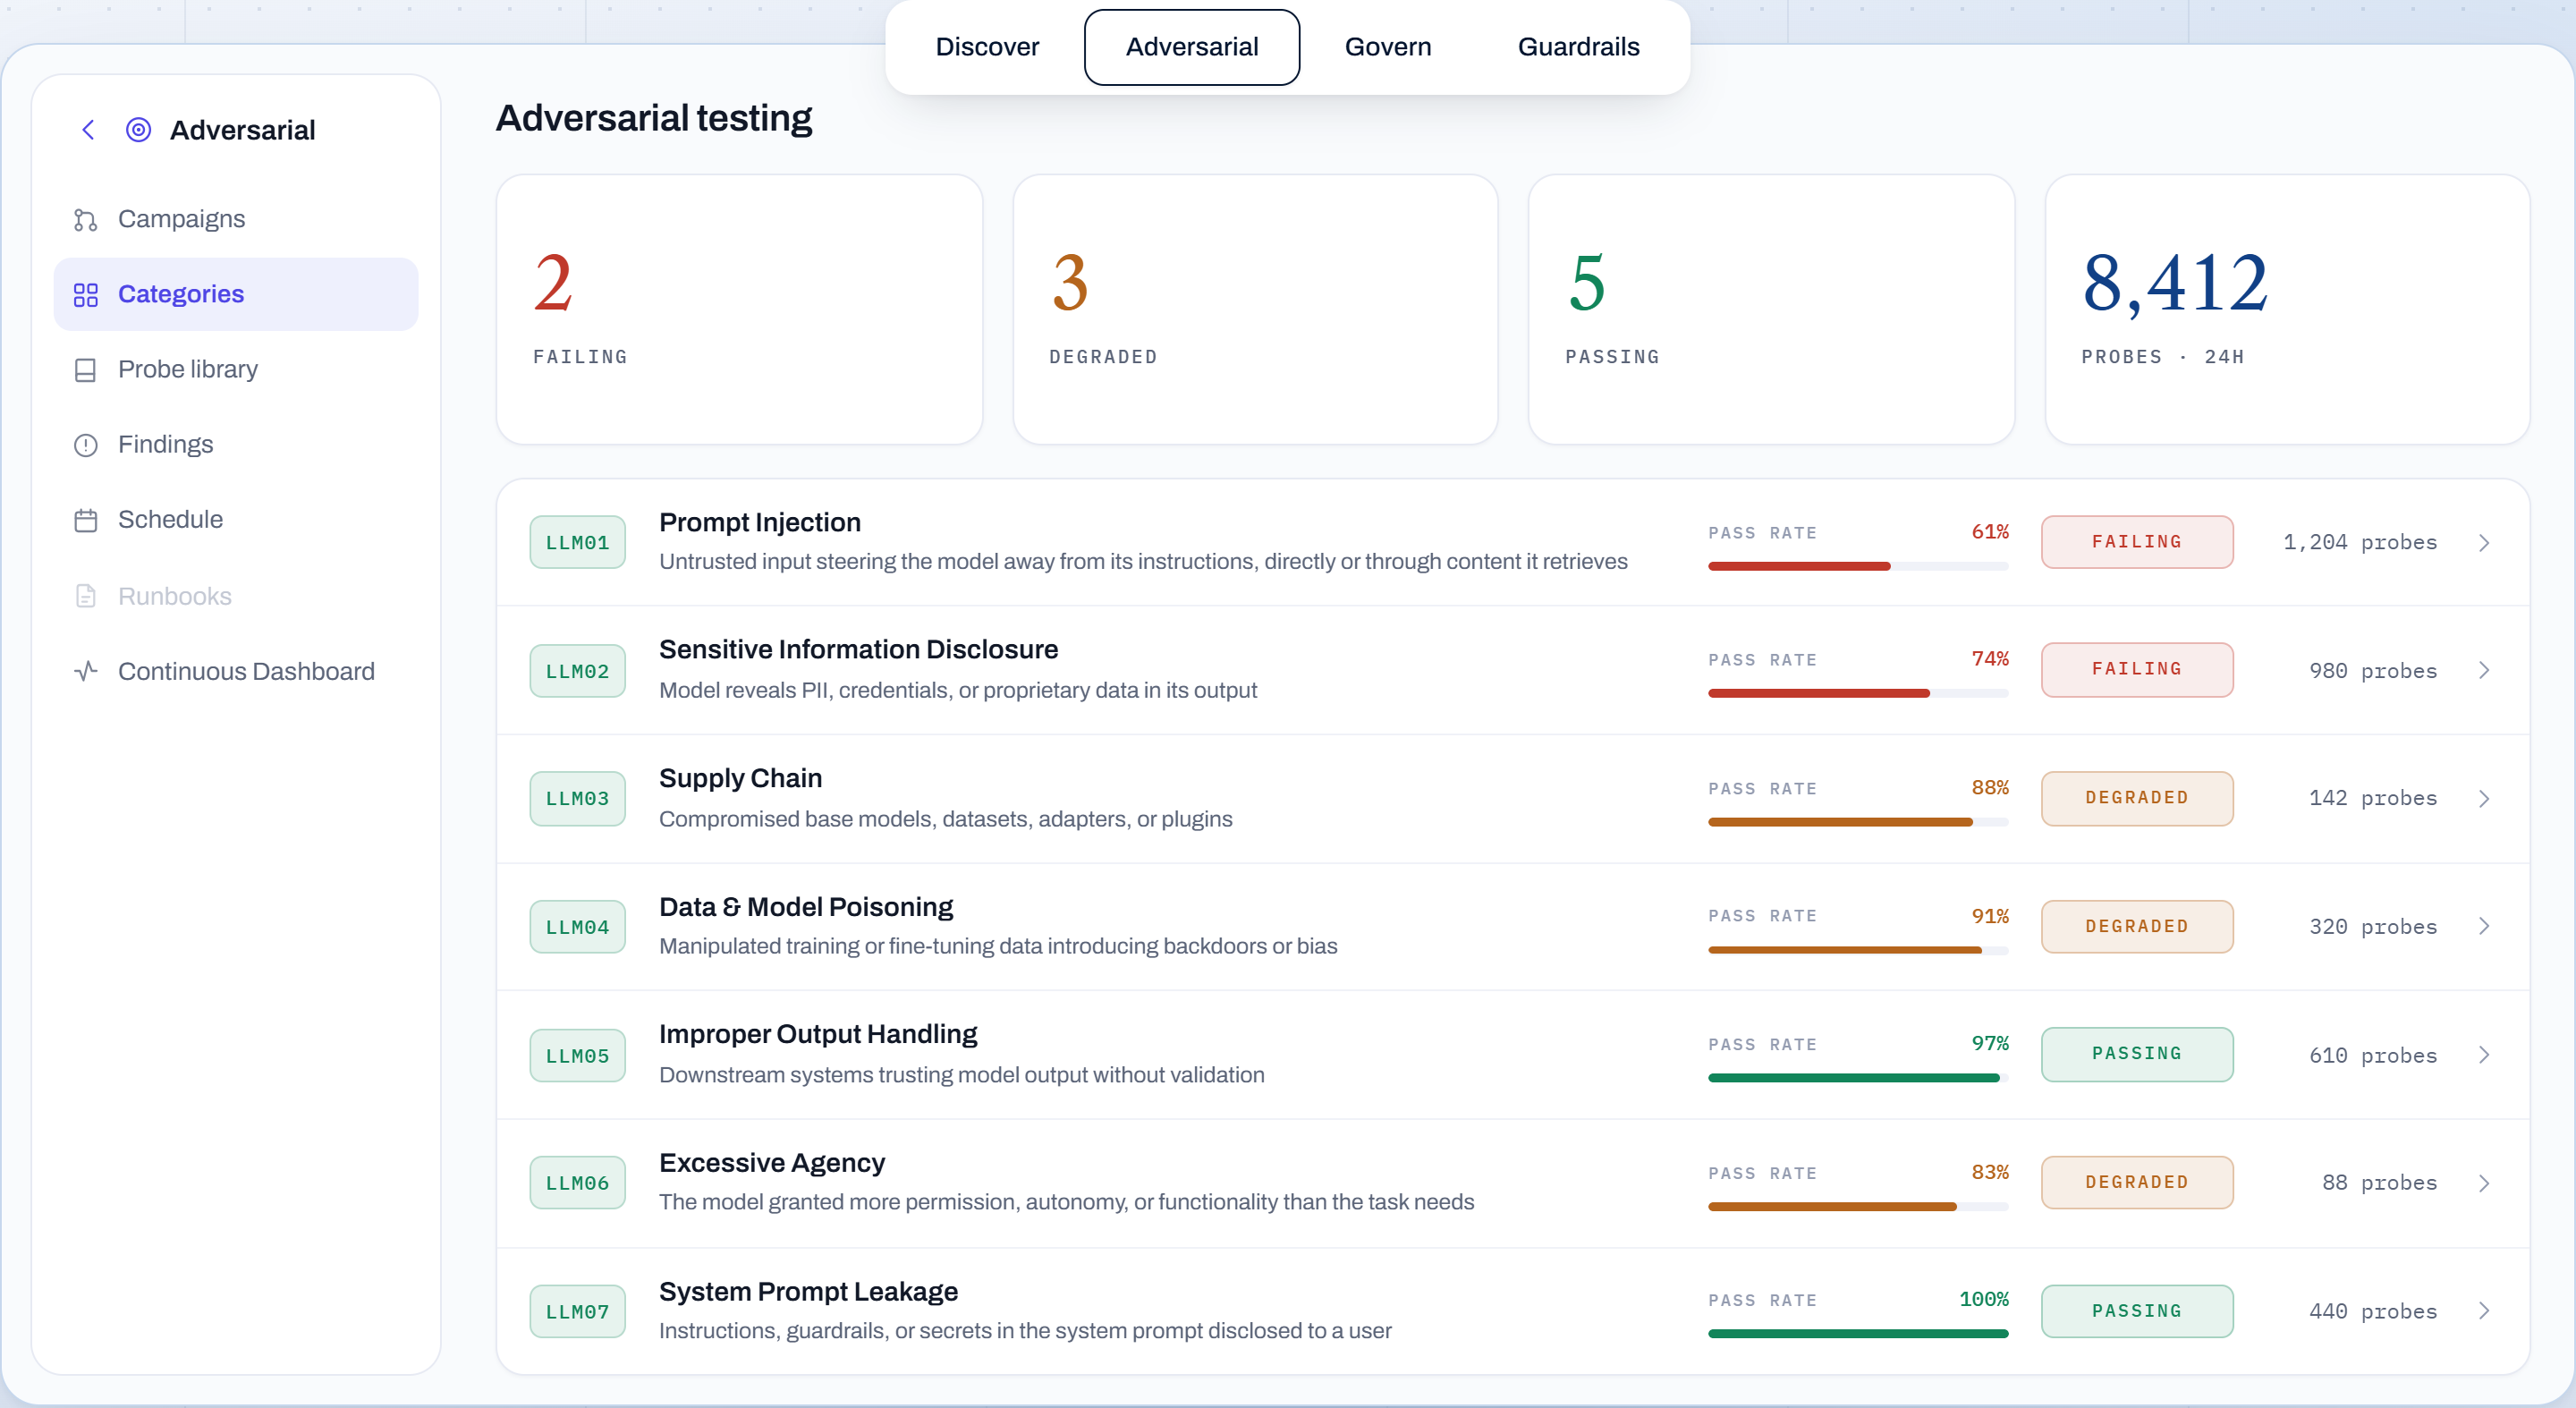
Attack Your Own System Before Someone Else Does
Most red-teaming happens once, months before launch, against a version of the system that no longer exists by the time it ships. Tahara AI runs the OWASP LLM Top 10 against staging on a recurring schedule, so a regression shows up the next cycle, not next year.
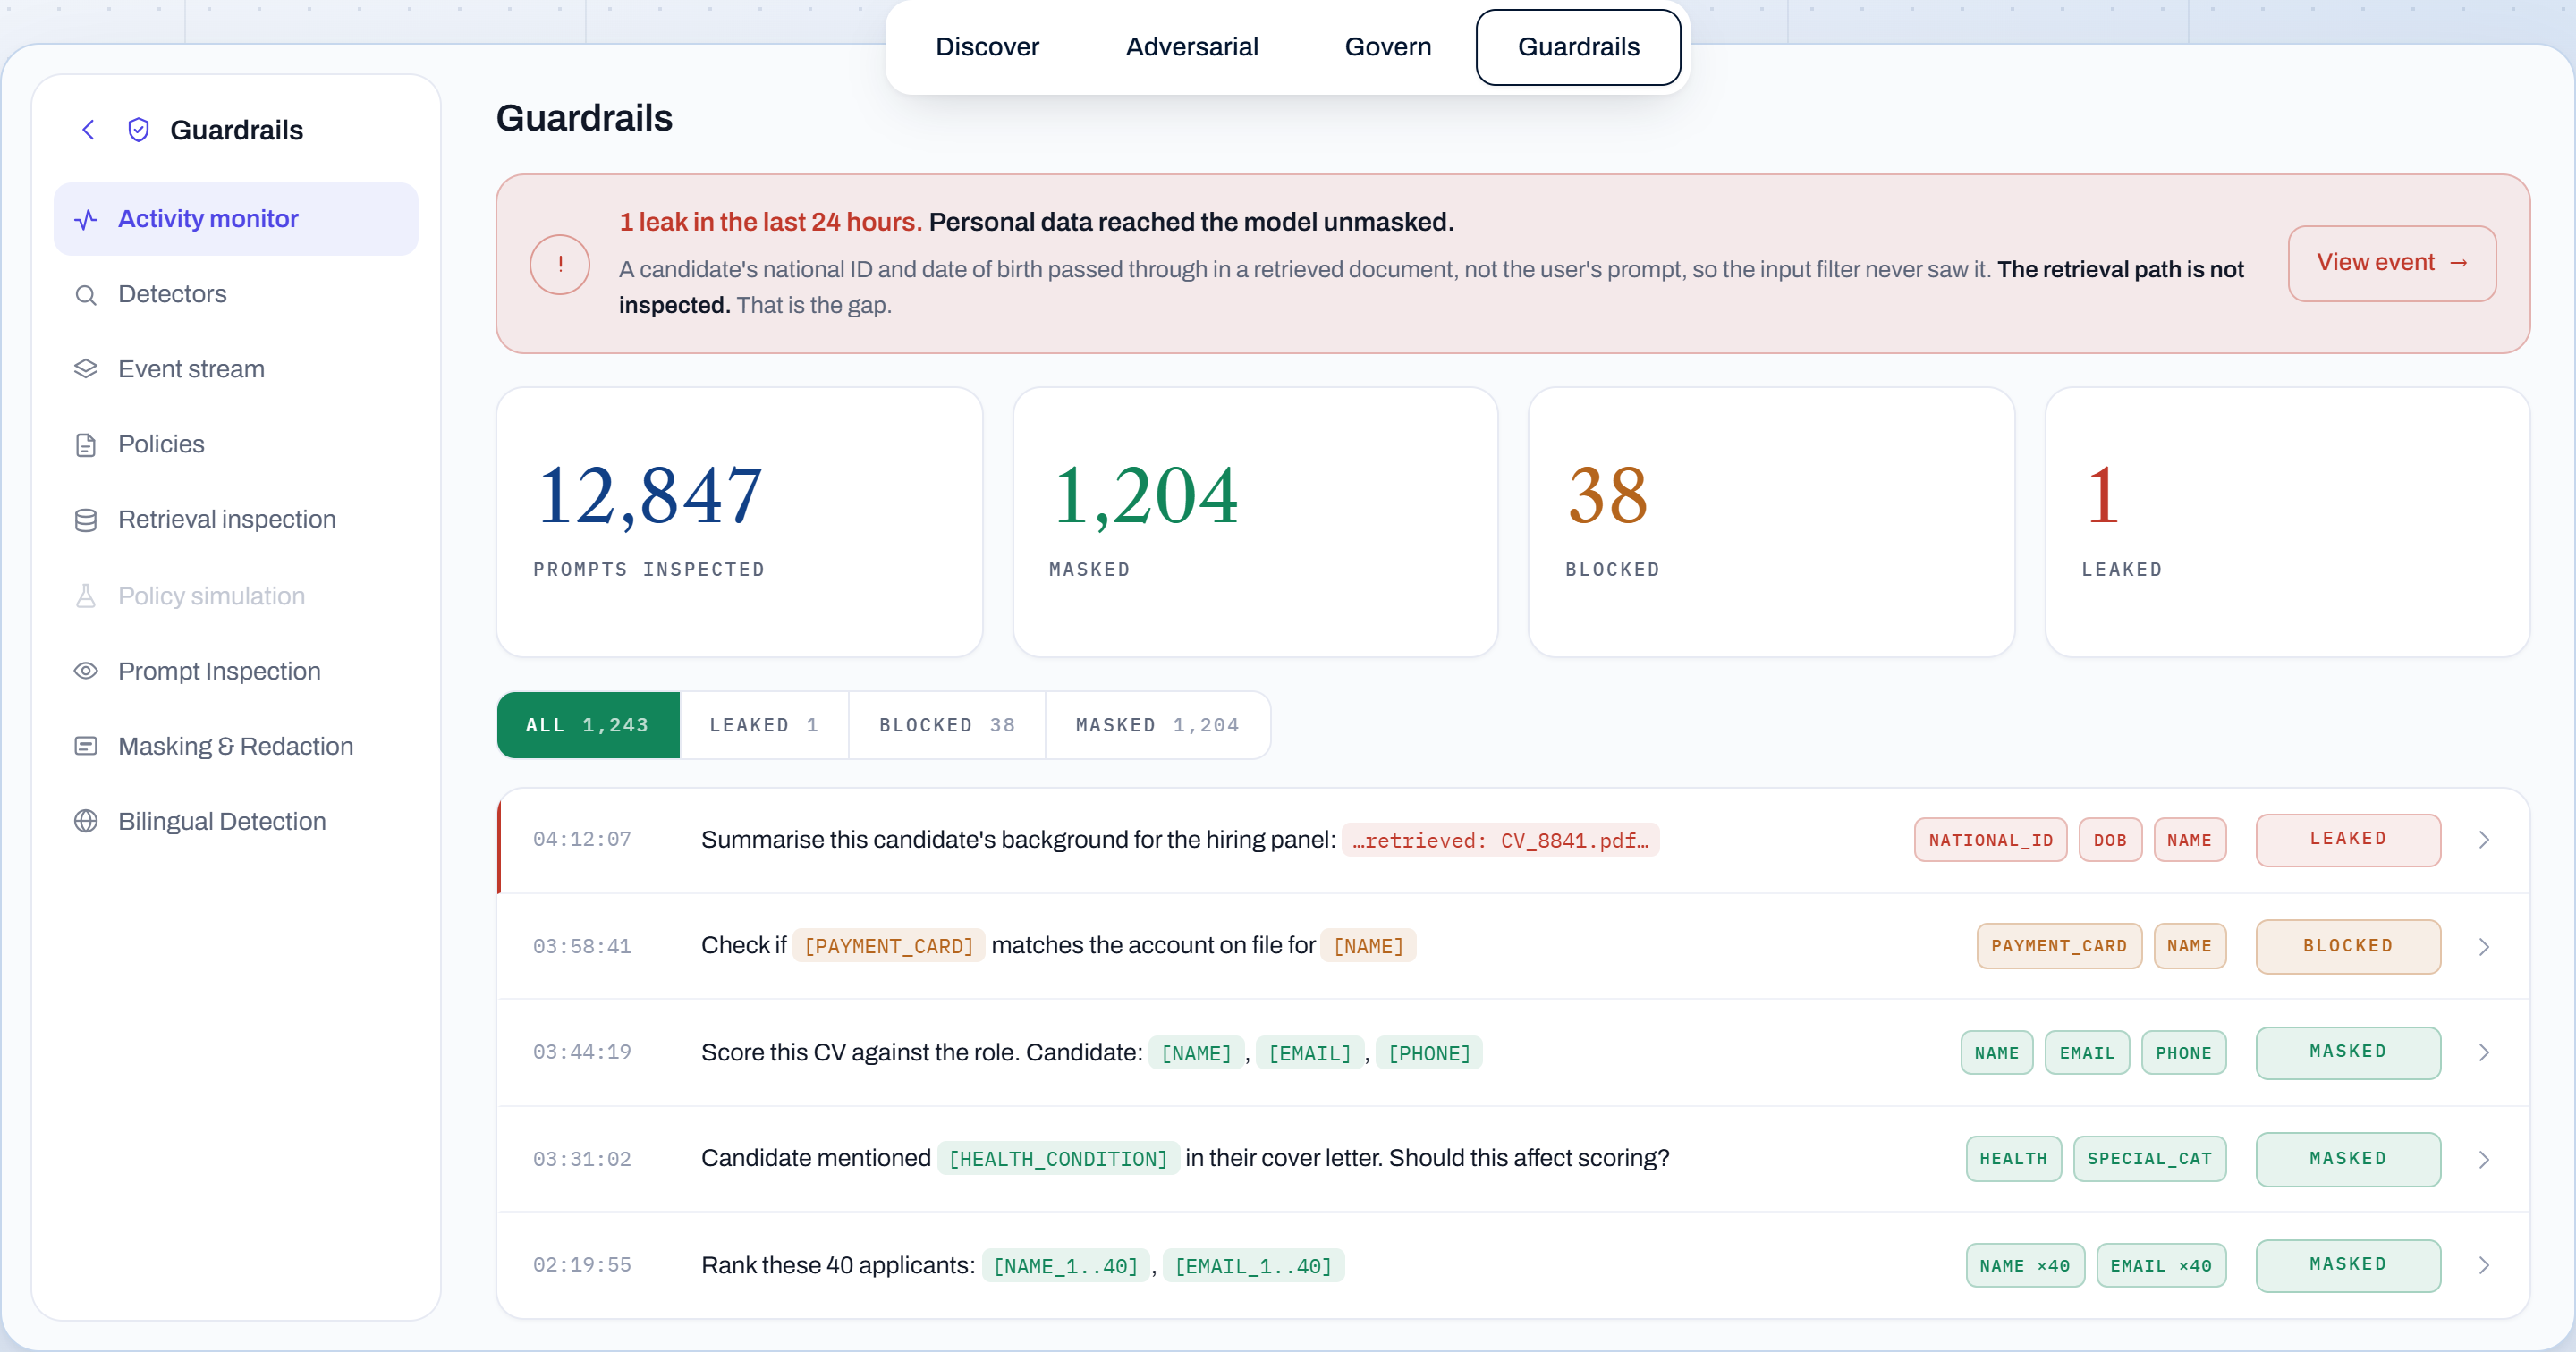
Catch What Leaks Before It Reaches the Model
By the time a privacy review catches a leak, it’s already happened. Guardrails inspect every prompt before it reaches the model, masking and blocking, bilingually in English and Roman Urdu, and logging the rare one that gets through.
Built Around One Framework, Not Twelve Separate Ones
What Actually Makes Tahara AI Different
Figures out exactly which laws and standards apply to a specific system, not a generic checklist.
Read-only, runs inside your boundary, never holds your credentials, has no inbound path back in.
Compares what a person said, what the policy states, and what the live system shows. The mismatch is the finding.
The OWASP LLM Top 10, run on a recurring schedule against staging, not a once-a-year pen test.
Prompt inspection and masking in English and Roman Urdu, before anything reaches the model.
Every piece of proof stored and dated, in a hash-chained record that can’t be edited after the fact.
Compliance is not a photograph. It is a live signal.
Discover every AI system in your environment, including the ones nobody remembered to log.
The full cycle re-runs automatically, so a change is caught within a day, not a year.
One evidence trail, the same record for your team, an auditor, or a regulator.
A machine’s observation can flag a problem. Only a person can close one.